Turn Claude Code into a security auditor that checks its own findings: Cloudflare's security-audit skill, installed in 2 minutes
TL;DR
What it is:
cloudflare/security-audit-skillis one agent skill that makes Claude Code run a six-phase security audit, where a different agent tries to disprove every finding.The key benefit: instead of a chat list of "consider adding input validation", you get a schema-checked
findings.jsonand a shortREPORT.md.Time to try: 2 minutes to install, 5 minutes for a first question. A full audit takes much longer and uses many tokens.
What it is
A skill is a folder with a SKILL.md file that Claude Code loads when your request matches it. According to Cloudflare's blog post, this skill is the seed of their internal vulnerability harness. This repo is the single-repo version you can run today.
The audit runs in six phases: map the code and trust boundaries, hunt with separate sub-agents, give each candidate to a fresh verifier, write findings.json and check it with a Node.js validator, re-verify the final records, and write the reports. The README's rule: "The agent that checks a finding is never the agent that found it."
Each record is one of three verdicts:
Verdict | Meaning |
|---|---|
| Full source trace, a bounded result, and a severity |
| The exact fact that is still missing; no severity |
| A candidate the verifier disproved |
Two design principles are worth copying even without the skill: "Severity requires impact", and "Defense-in-depth gaps are not vulnerabilities".
How active is it?
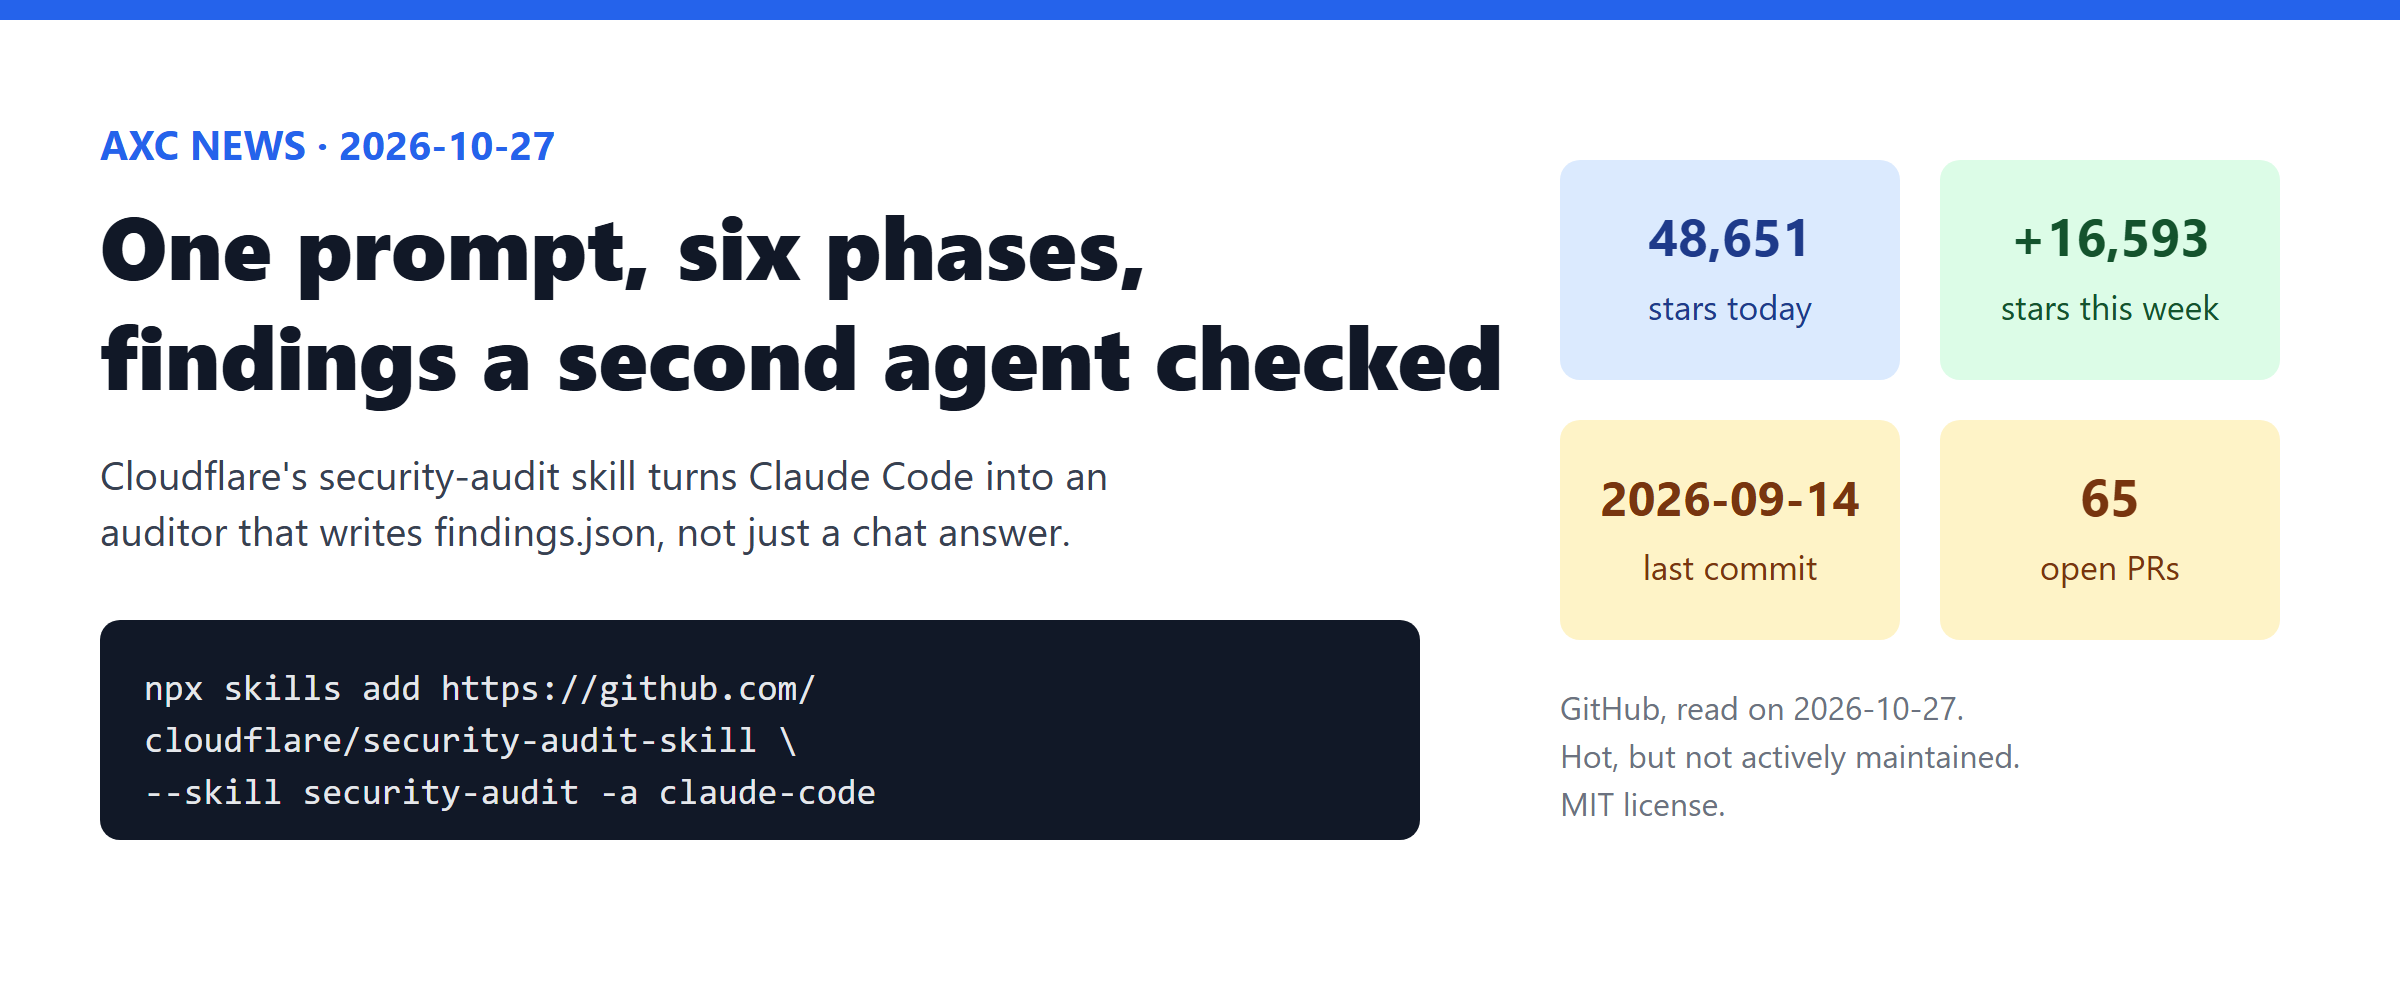
Read from GitHub on 2026-10-28: 50,169 stars (+1,518 since yesterday), 3,150 forks, MIT license. But the last commit on main is from 2026-09-14, there are no releases, and no pull request has been merged since 2026-09-10. 66 pull requests and 33 issues are open.
So it is very popular, but not maintained right now. Treat it as a well-designed snapshot, not a supported product.
Try it in 5 minutes
Prerequisites: Claude Code, Node.js (for the Skills CLI and the validators), and a repo you are allowed to send to the model.
Install the skill for your user (from the README):
npx skills add https://github.com/cloudflare/security-audit-skill --skill security-audit --globalIf the CLI asks which agents to install for, pick Claude Code (npx skills --help lists the agent-selection options).
Open Claude Code in the repo you want to audit, and ask a focused question first:
   cd path/to/your-repo
   claude
   > find security vulnerabilities in ./src
For a full audit with your own output folder, use another README prompt:
> do a security review, output to ~/audits/my-project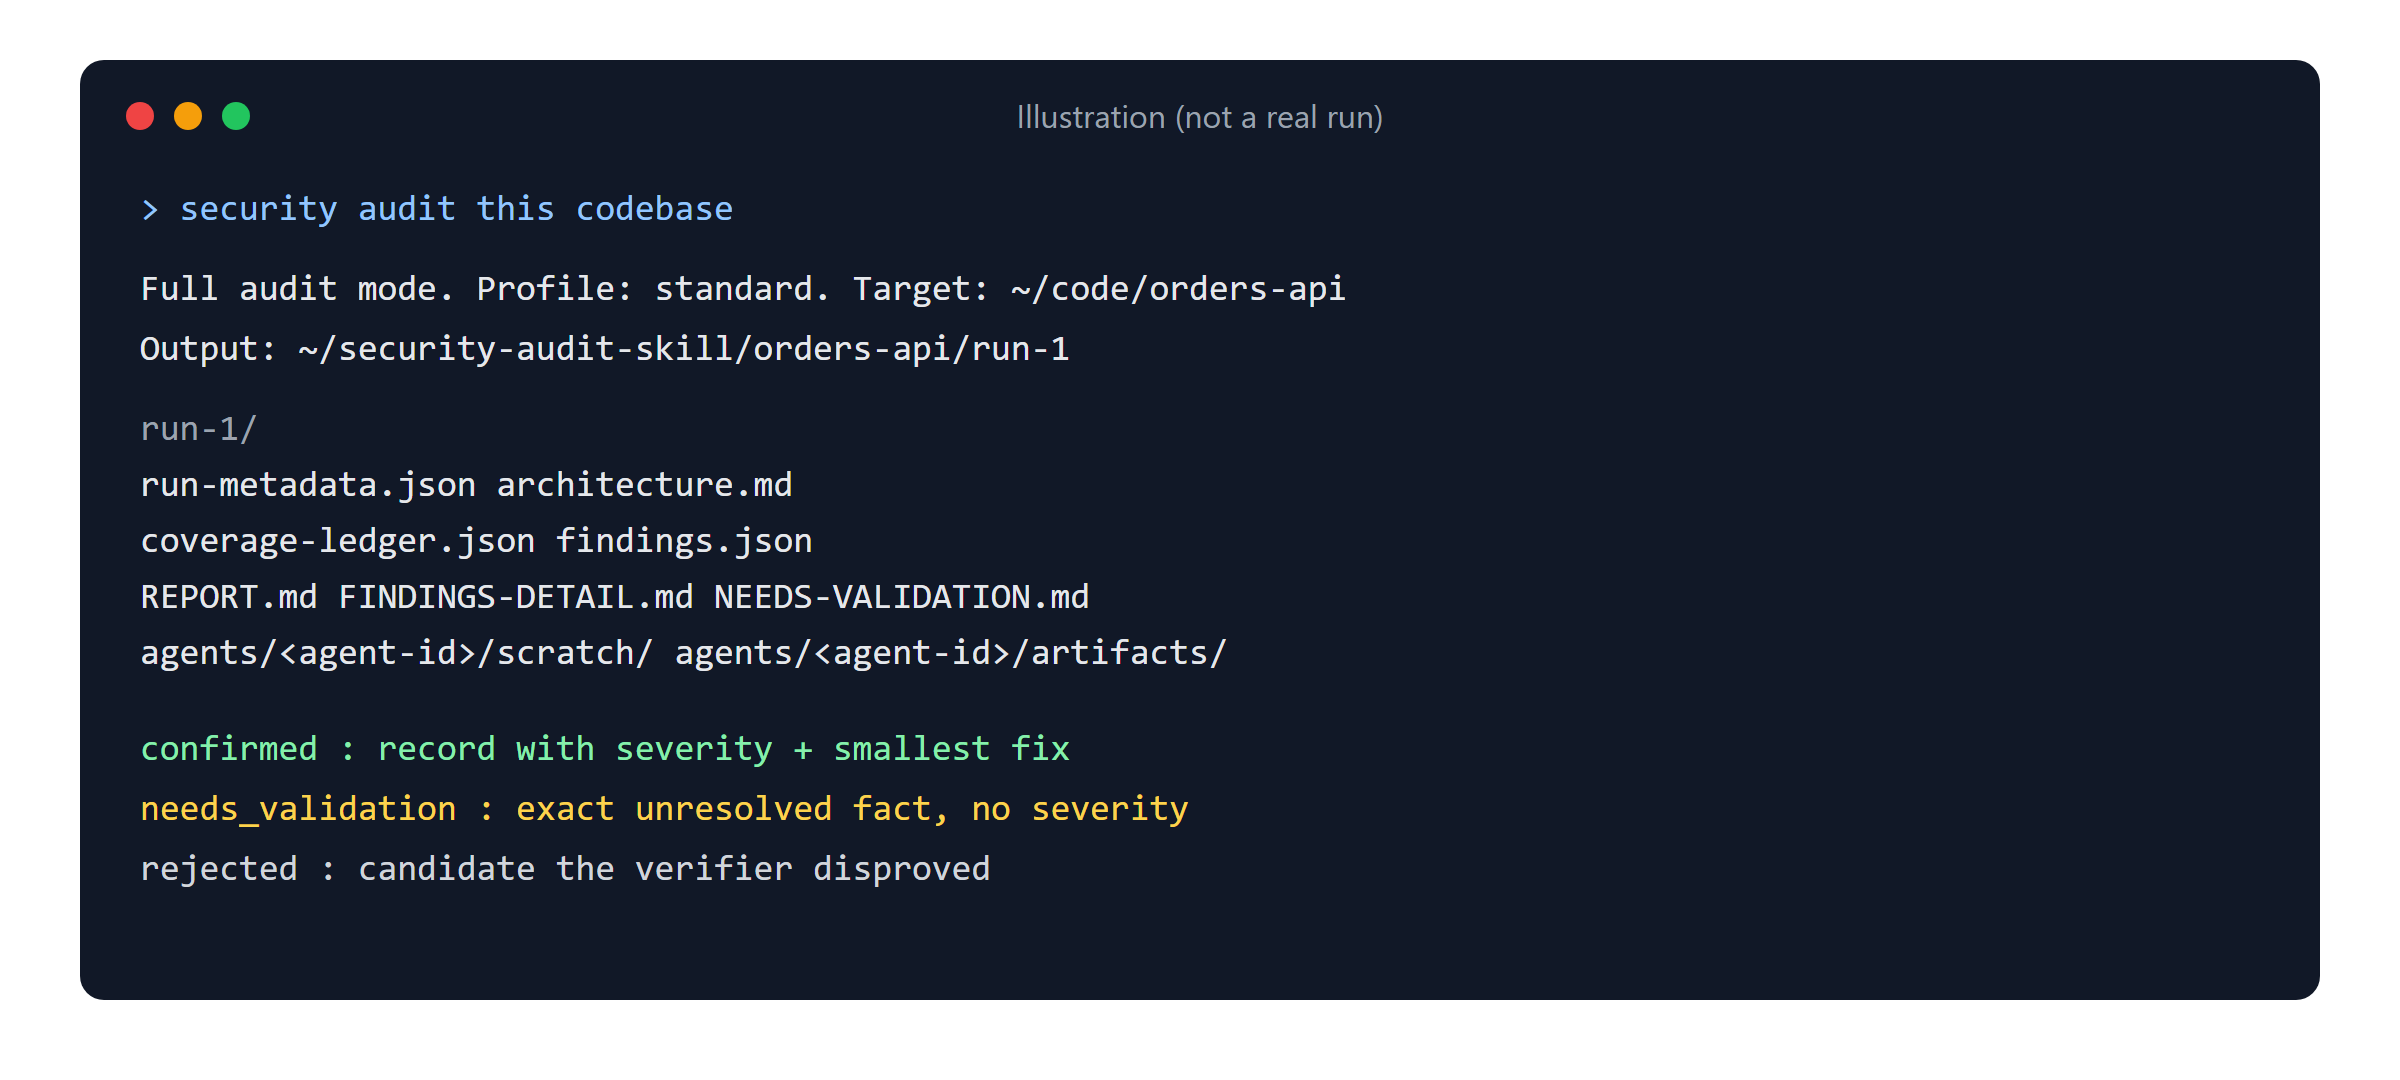
What you will see: a focused question gets a normal answer in "guidance mode". A clear audit request starts "full audit mode" and writes its files to ~/security-audit-skill/<repo-name>/run-<N> by default, outside your repo. Open REPORT.md first. Runs are additive: the next run reuses the earlier ledger and targets the gaps.
Caveats
Not maintained right now. No merge in seven weeks; you get what is on
maintoday.Validators fail on native Windows (issue #53, still open). Run full audits in WSL2.
Your code goes to the model. Every hunter and verifier reads source. Check company policy and the client contract before you use it on a client repo.
It costs a lot more than one prompt. A full audit runs many sub-agents in waves. Name a folder, not the whole monorepo.
No recall promise. The README says one run found about half of what repeated runs found. A clean report does not mean "secure", and it does not replace a pen test.
No sandbox, no execution. Without an OS-enforced sandbox, the skill will not run target code, so more leads stay
needs_validation.
Sources
https://github.com/cloudflare/security-audit-skill (README, stars, forks, commits, open PRs and issues, read 2026-10-28)
https://github.com/cloudflare/security-audit-skill/issues/53
https://blog.cloudflare.com/build-your-own-vulnerability-harness