Use the Claude Code extension in Cursor? Check your machine for the 2.1.312 / 2.1.313 backdoor in 2 minutes
TL;DR
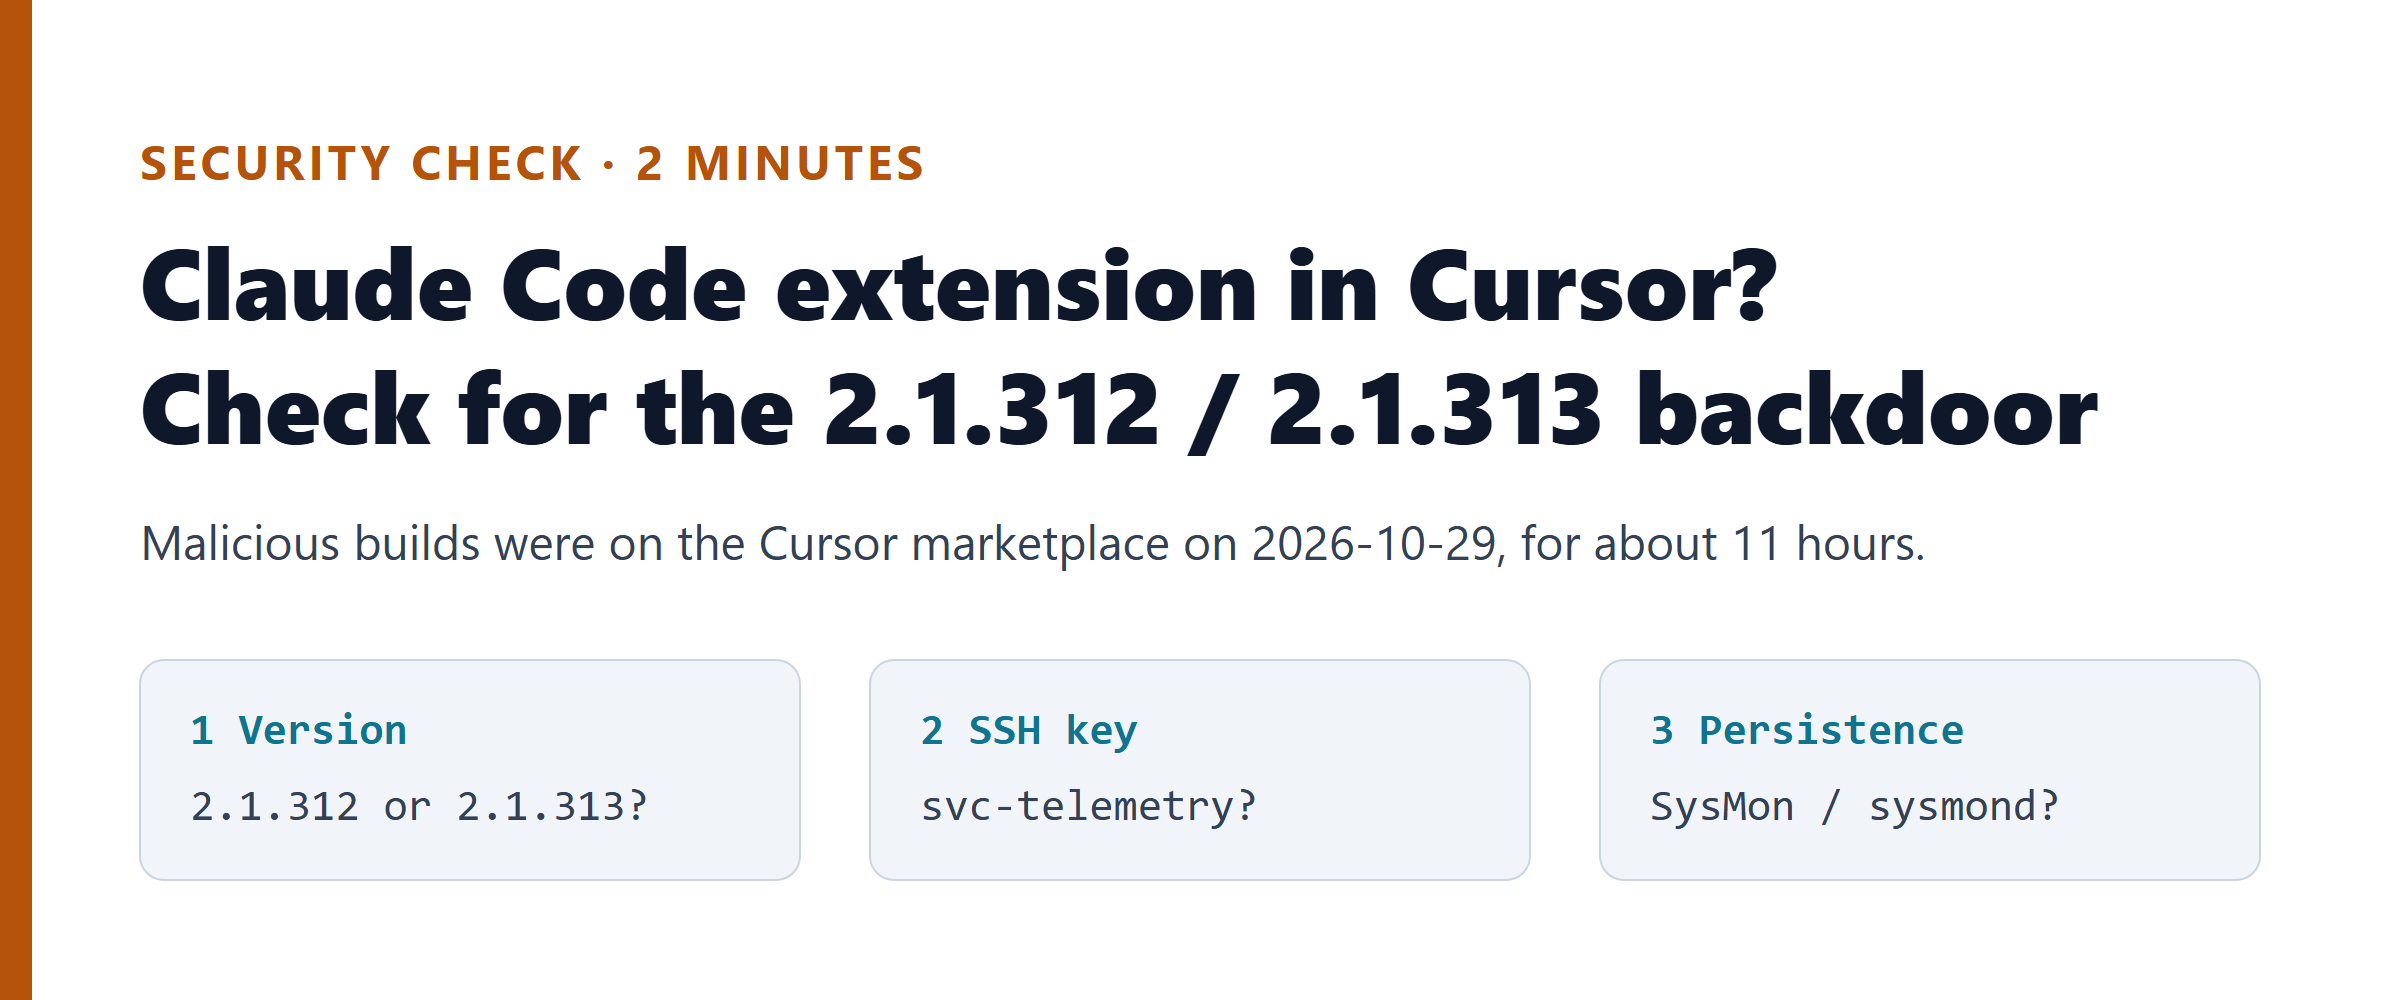
On 2026-10-29, malicious builds of the Claude Code extension (versions 2.1.312 and 2.1.313) were on the Cursor marketplace for about 11 hours.
They tried to plant an SSH key and a reverse tunnel. Updating or uninstalling does not remove that.
Three copy-paste checks tell you if your machine is clean: about 2 minutes.
What it is
If you use Cursor, it installs VS Code extensions from its own marketplace, not from Microsoft's. According to Cursor's security notice, someone published modified builds of Anthropic.claude-code 2.1.312 and 2.1.313 there, for macOS and Windows. Cursor says the builds "were not developed by Anthropic", and it estimates up to 5,000 users may be affected (as reported by YourStory).
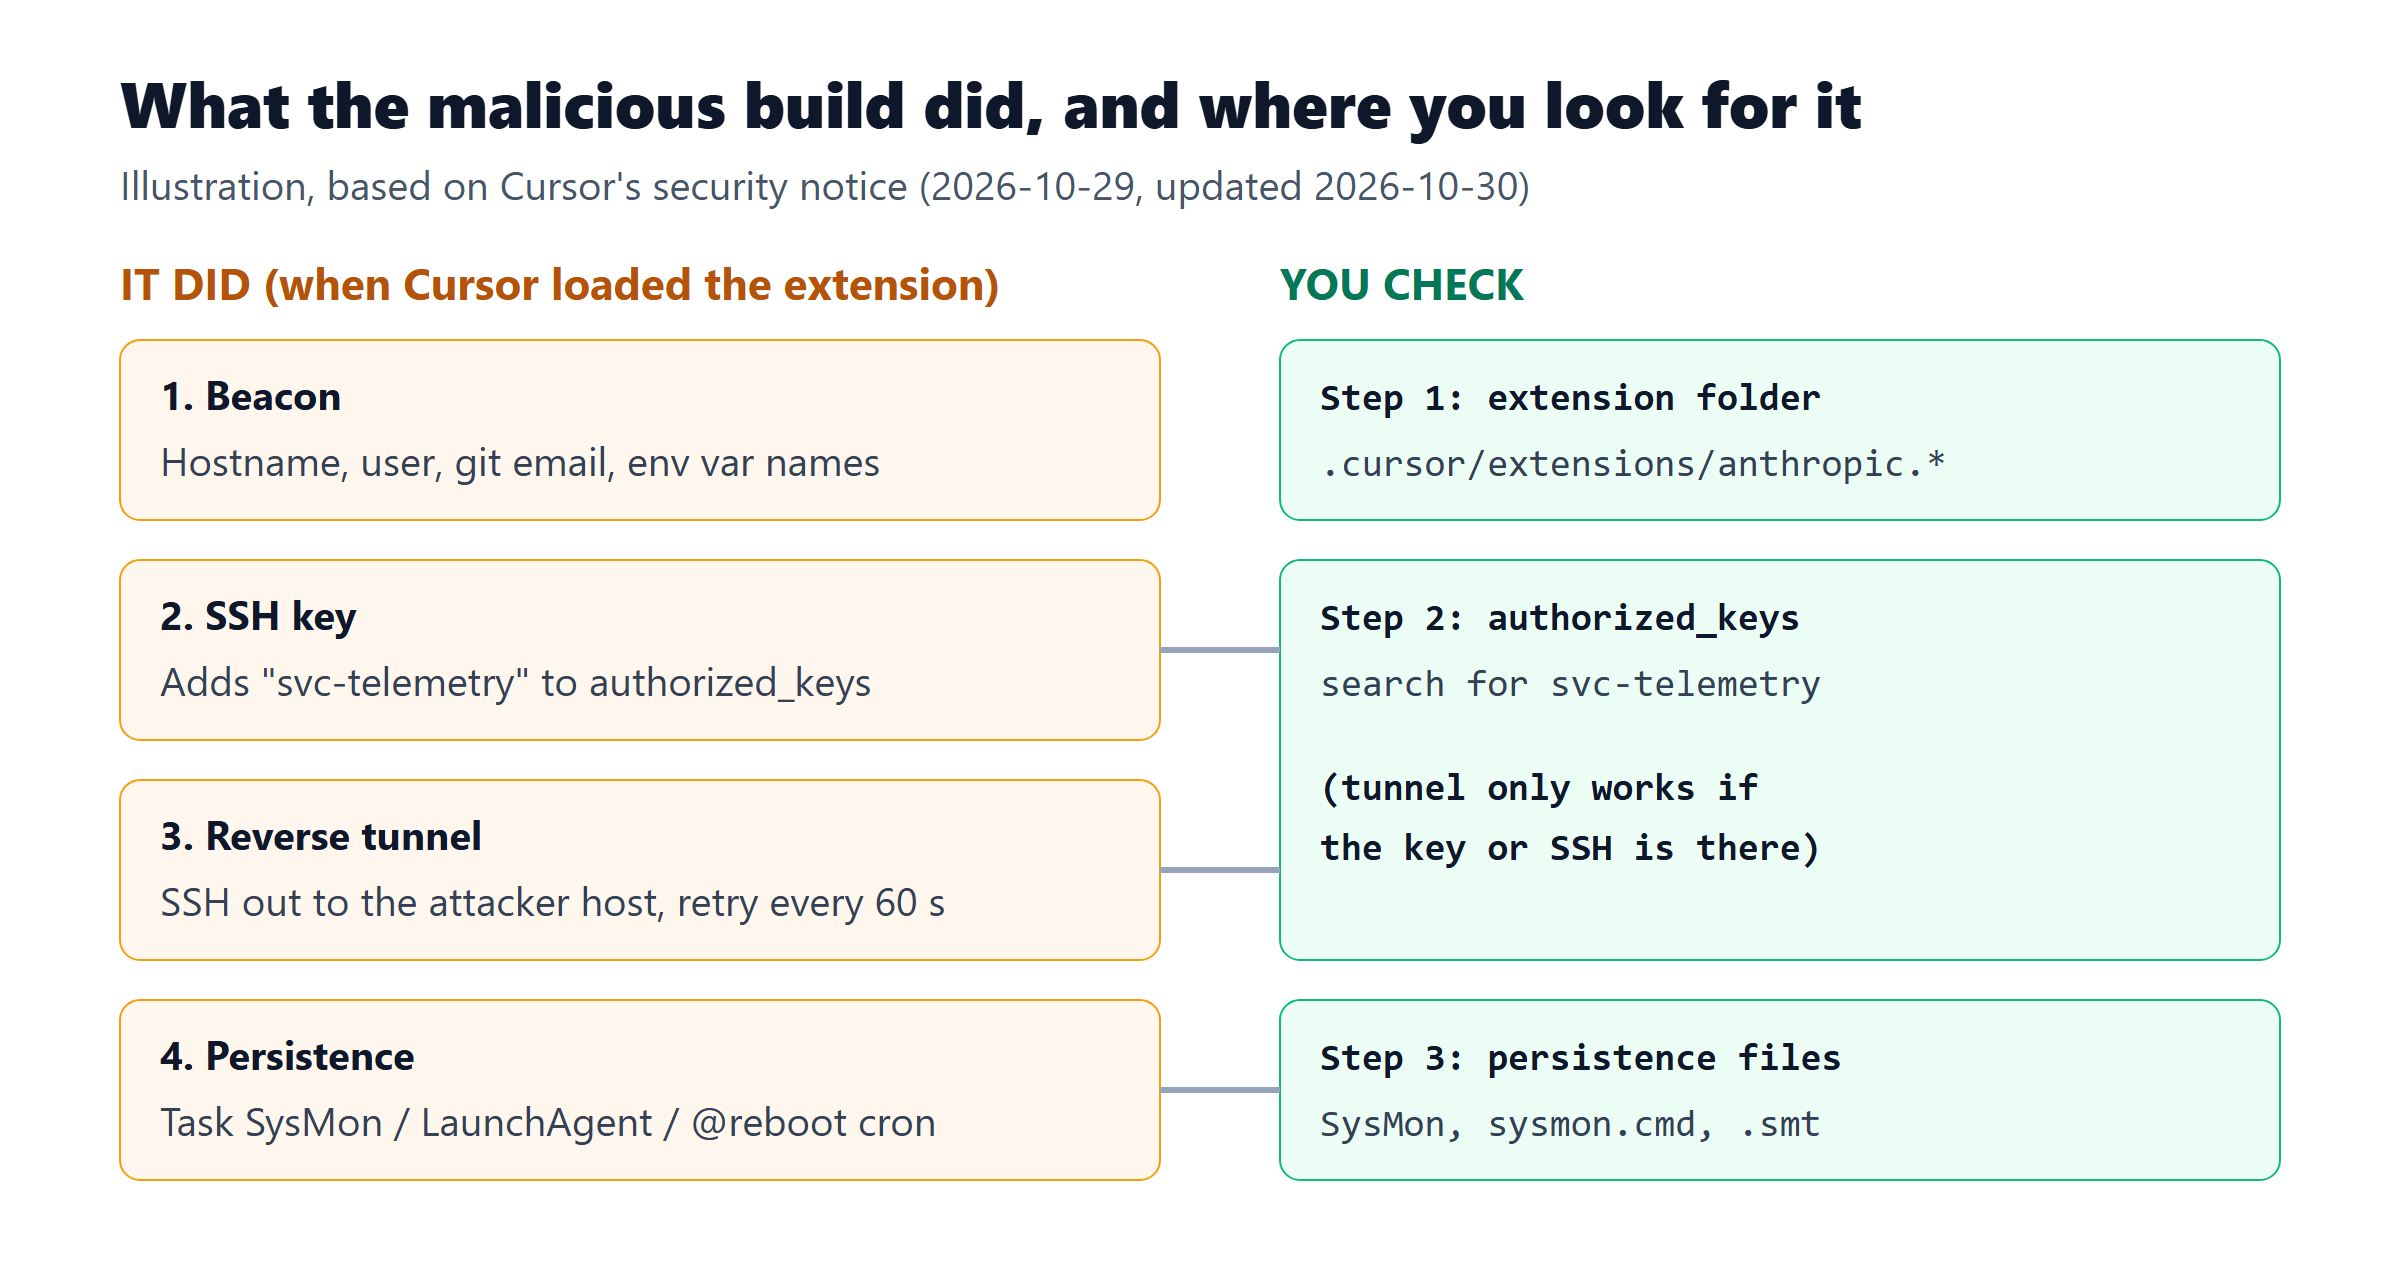
The bad code ran as soon as Cursor loaded the extension. No click needed. According to Cursor and the Phorion advisory, it did four things:
Sent a beacon: hostname, user name, OS, public IP, git email, and the names (not values) of environment variables like
*TOKEN*or*SECRET*.Added an attacker SSH key labeled
svc-telemetrytoauthorized_keys.Opened a reverse SSH tunnel to
134.209.82.225, retrying every 60 seconds.Made itself persistent: scheduled task
SysMonon Windows, LaunchAgentcom.apple.sysmondon macOS.
Cursor says the SSH parts usually fail without admin rights, and the attacker server is now offline. The beacon still went out.
Illustration
Try it in 5 minutes
Prerequisites: a terminal on the machine where you use Cursor. No install needed.
Step 1: See which Claude Code versions Cursor installed.
# Windows PowerShell
Get-ChildItem $HOME\.cursor\extensions -Filter anthropic.claude-code*
# macOS / Linux
ls ~/.cursor/extensions | grep anthropic.claude-codeA folder named anthropic.claude-code-2.1.312-... or ...-2.1.313-... means you had a bad build. Run step 2 anyway: an auto-update may have removed the old folder.
Step 2: Search for the attacker's SSH key (the check from Cursor's notice).
# Windows PowerShell
Select-String -Path "$HOME\.ssh\authorized_keys" -Pattern svc-telemetry
Select-String -Path "C:\ProgramData\ssh\administrators_authorized_keys" -Pattern svc-telemetry
# macOS / Linux
grep -qs svc-telemetry ~/.ssh/authorized_keys && echo "KEY FOUND" || echo "not impacted"Step 3: Read the result, then check for persistence.
# Windows PowerShell
Get-ScheduledTask -TaskName SysMon -ErrorAction SilentlyContinue
Test-Path "$env:APPDATA\Microsoft\Windows\Start Menu\Programs\Startup\sysmon.cmd", "$HOME\.config\smt.cmd"
# macOS
ls ~/Library/LaunchAgents/com.apple.sysmond.plist ~/.config/.smt 2>/dev/nullWhat you will see: no output, "not impacted" and False mean you are not affected. Found anything? Disconnect, tell your security team, run Cursor's clean-up script (linked in its notice), and rotate the keys and tokens on that machine.
Tip: Update the extension to 2.1.314 or later. According to Cursor and the published reports, the builds on the Microsoft VS Code Marketplace, Open VSX and the npm CLI were not affected. Open VSX shows 2.1.316 today.
Caveats
Updating is not cleaning. Cursor warns that uninstalling "may not be sufficient". The key and the scheduled task stay until you remove them.
Root cause is not public. Neither Cursor nor Anthropic has explained how the builds reached the marketplace.
Read scripts before you run them. Cursor's Windows script needs an Administrator PowerShell. Open it and read it first.
Env var names leaked even on clean machines. If you had a bad build, assume the attacker knows which secrets you have, and rotate them.
VS Code users: you are not in scope, according to Cursor. The checks still take 2 minutes.
Claude Quick Hits
Claude Code 2.1.316 (2026-10-31):
CLAUDE_CODE_SUBAGENT_EFFORTsets the effort level for subagents;CLAUDE_CODE_DISABLE_ULTRATHINKturns the keyword off.Fast mode for Opus 4.8 is deprecated (2026-10-30): removal on 2026-11-30. Move fast-mode calls to Opus 5.5.
AI Tool Radar
Repo/Tool | What it does (1 line) | Stars (growth) | Quick try |
|---|---|---|---|
Plugin that learns from past sessions to cut coding-agent cost (18.4–30.9% on SWE-Bench, according to the README) | 3,968 (new, created 2026-10-13) |
| |
Claude Code or Codex draws an interactive map of your codebase | 1,818 (+1,425 since 2026-10-30) |
|
Sources
https://cursor.com/blog/claude-code-extension-security-notice
https://phorion.io/blog/offical-claude-code-vsx-compromise/
https://news.ycombinator.com/item?id=50300683
https://yourstory.com/ai-story/cursor-warns-of-malicious-extension-affecting-up-to-5000-users
https://open-vsx.org/extension/Anthropic/claude-code
https://github.com/anthropics/claude-code/blob/main/CHANGELOG.md
https://platform.claude.com/docs/en/release-notes/overview
https://github.com/microsoft/TokenEconomizer
https://github.com/haydenschmitty/floorplan